watchTowr traced a new authentication bypass and Scan-to-Fax code-execution chain through an interim PaperCut build. Check the running version and past access to its web interface.
A remote execution path depends on Dynamic Method Invocation. Identify reachable Struts 2 apps, disable that feature or move to an Apache-listed fix, and triage exposure.
Microsoft's research shows how bug volume can overwhelm validation and release work. Check affected dependency builds and carry reproducible findings through a shipped fix.
CISA lists an exploited image-upload traversal in ONLYOFFICE Document Server before 5.6.3. Find older JWT-enabled servers, update them and check their exposure.
Unit 42 maps contract reads, transaction data and zero-value transfers used by poisoned packages. Correlate runner processes with blockchain traffic and restrict unneeded egress.
An unauthenticated file read reaches known paths inside eight Atlassian server products. Match installed branches to fixes and review decoded access logs.
Two crafted-PDF flaws affect Foxit Reader and Editor. Check both CVEs against installed platforms and releases, then verify Foxit updates on endpoints.
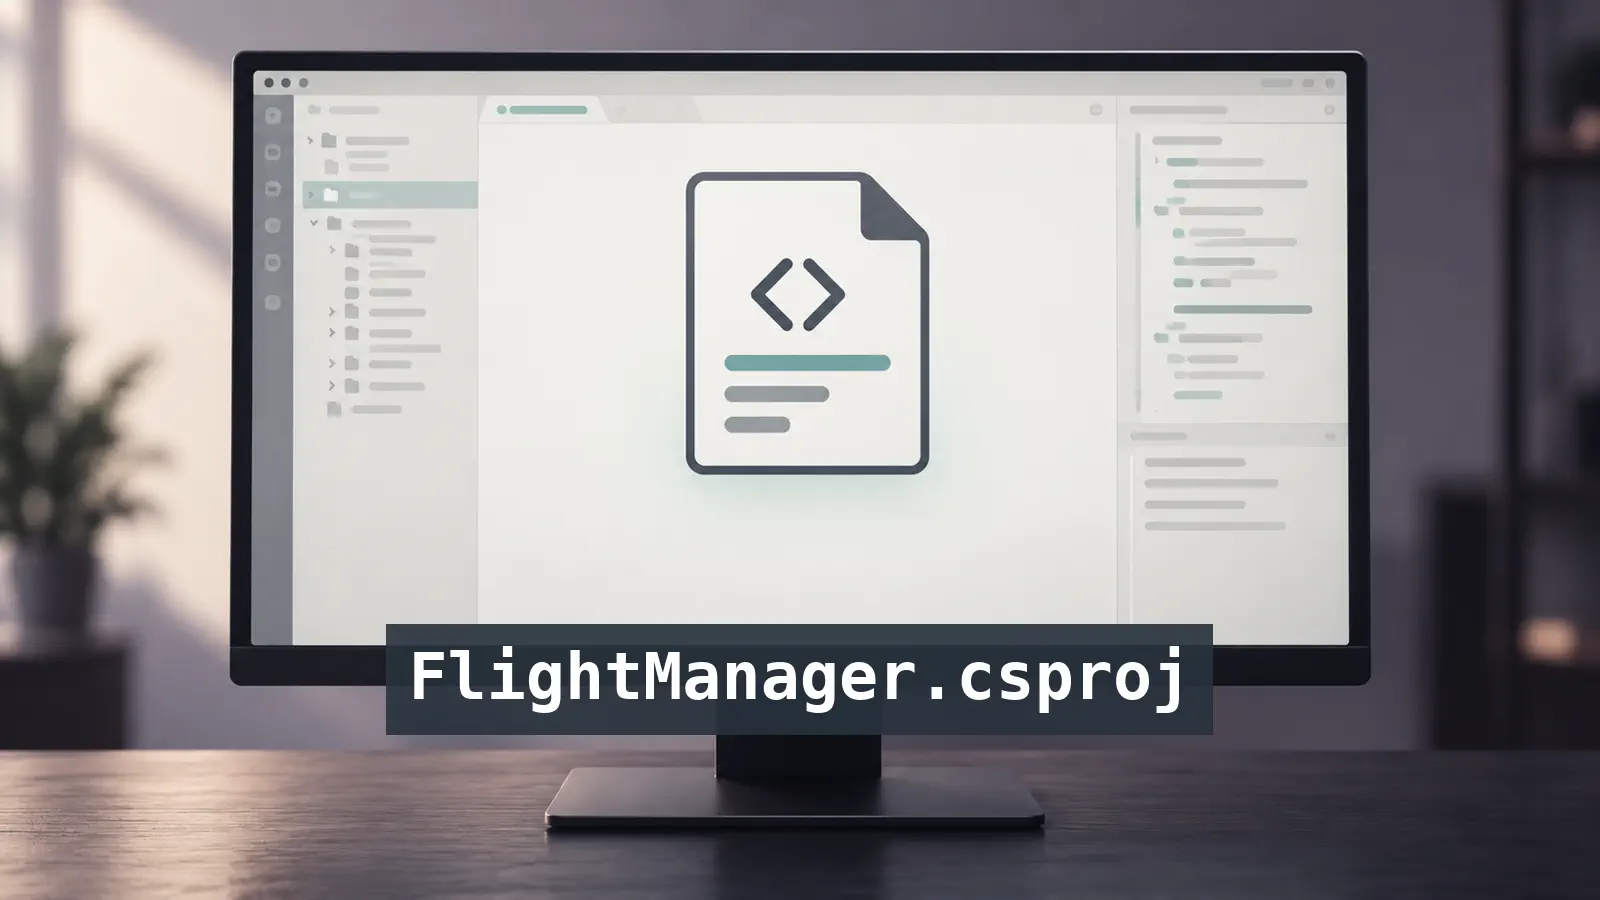
A fake Dubai Airports coding test ran from a Visual Studio project before compilation. Inspect the project target and developer-host staging path, then isolate matches.
Readwise Reader 8.10.1 fixes an SVG sanitizer flaw, while two metadata XSS records still include that build. Check Android versions and limit untrusted imports.
CISA describes file upload and possible code execution; WSO2 describes a JWT bypass and account takeover. Check product builds and reconcile the attack path with WSO2.
CISA lists an exploited session flaw with code execution as the Zammad user. Zammad says 6.5 and older are exploitable; move those installations to 7.2.0 and triage exposure.
An ownership check is missing from four multi-user chat handlers through v0.12.0. Limit account access and review cross-user conversation activity while awaiting a verified fix.