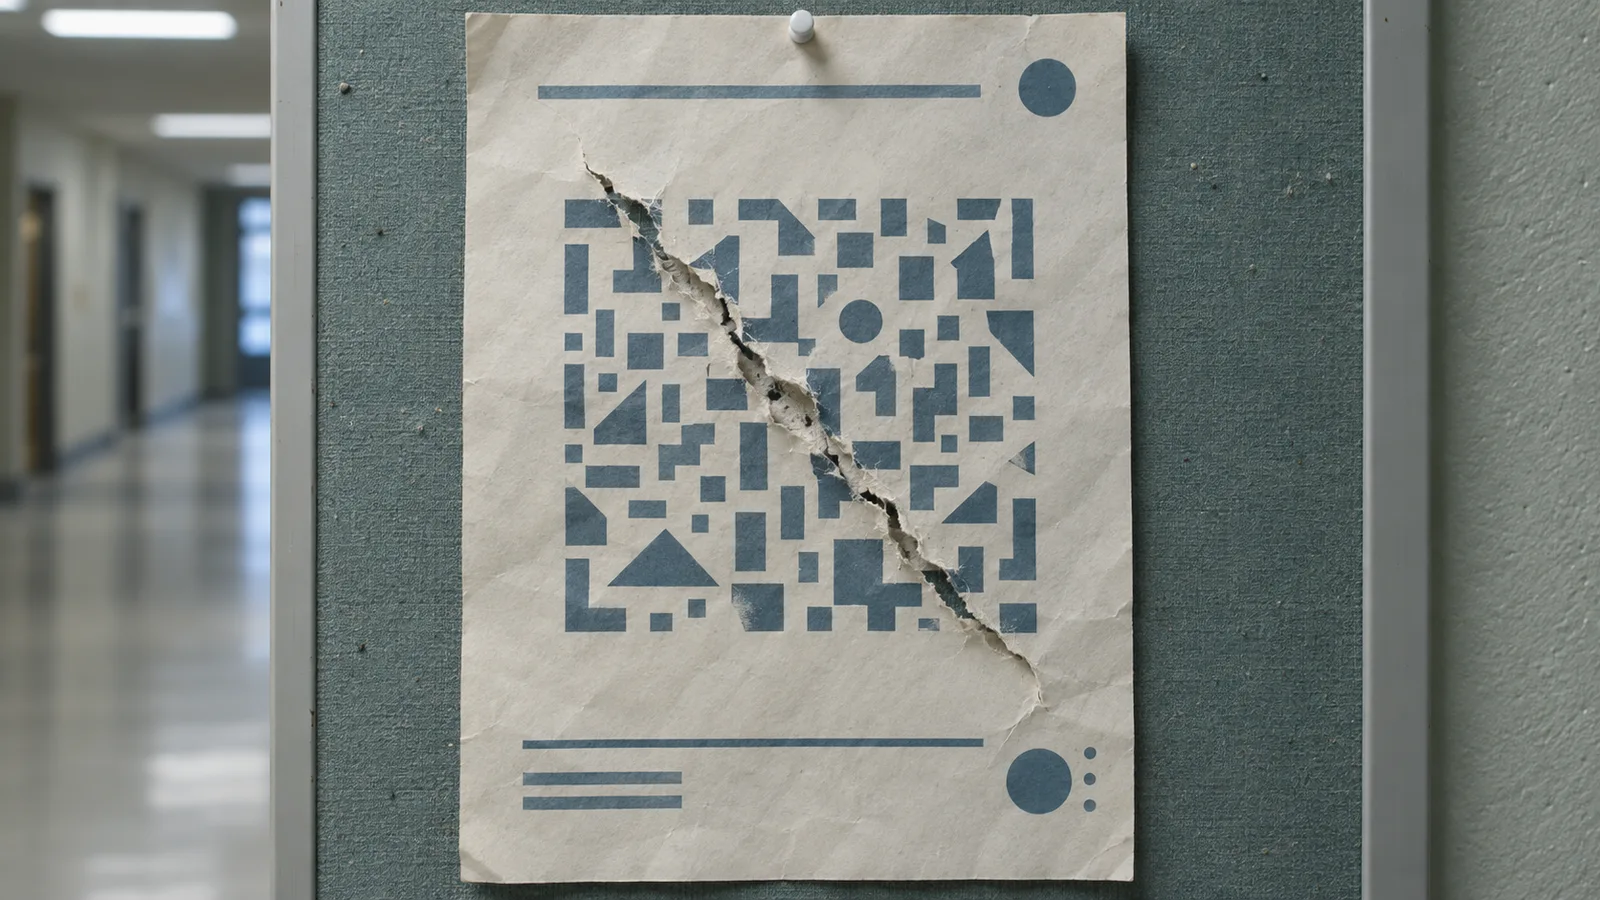
Fake event invites target Taiwan researchers’ Google accounts
Talos traced event invitations and altered poster QR codes to a live Google sign-in relay. Inspect the actual registration destination and review affected accounts.
Read article →Reader view
Choose the default article length.
Threat actors, malware campaigns, phishing, exploitation, and incident activity.
Talos traced event invitations and altered poster QR codes to a live Google sign-in relay. Inspect the actual registration destination and review affected accounts.
Read article →Two Apex npm tools fetch executables and attacker-selected commands; one also sends coding-agent conversations to an Apex server. Find the tools and revoke exposed secrets.
Read article →Plaintext instructions in malware samples shifted some model triage toward benign. Search extracted strings and keep sample text out of the scanner's instruction channel.
Read article →In a Windows ClickFix case, endpoint-side termination stopped repeated command pastes; check enforce mode and the process tree before treating an alert as a block.
Read article →ProFTPD's mod_copy flaw lets remote attackers read and write arbitrary files. Check reachable FTP services, command logs and distribution patches.
Read article →A backup management server became a SYSTEM-level foothold. Restrict its web interface and hunt for a fake Edge service, JSP shells and miner traffic.
Read article →A crafted TKEY query can stop vulnerable BIND DNS servers before access controls run. Check the running build and install the vendor's patched package.
Read article →Unit 42 traced an exploited NetScaler command-injection chain through two appliance logs into a disguised PHP shell. Preserve logs and inspect the web-server configuration.
Read article →A remote execution path depends on Dynamic Method Invocation. Identify reachable Struts 2 apps, disable that feature or move to an Apache-listed fix, and triage exposure.
Read article →CISA lists an exploited image-upload traversal in ONLYOFFICE Document Server before 5.6.3. Find older JWT-enabled servers, update them and check their exposure.
Read article →Huntress reconstructed an Akira attack from Shellbags, ransomware logs and shadow-copy events after its endpoint agent arrived too late to record the launch.
Read article →Unit 42 maps contract reads, transaction data and zero-value transfers used by poisoned packages. Correlate runner processes with blockchain traffic and restrict unneeded egress.
Read article →A Power BI report link sent targets to a fingerprinting page and a delayed installer. Hunt for both remote clients and the recurring repair task.
Read article →Showing 14–26 of 156