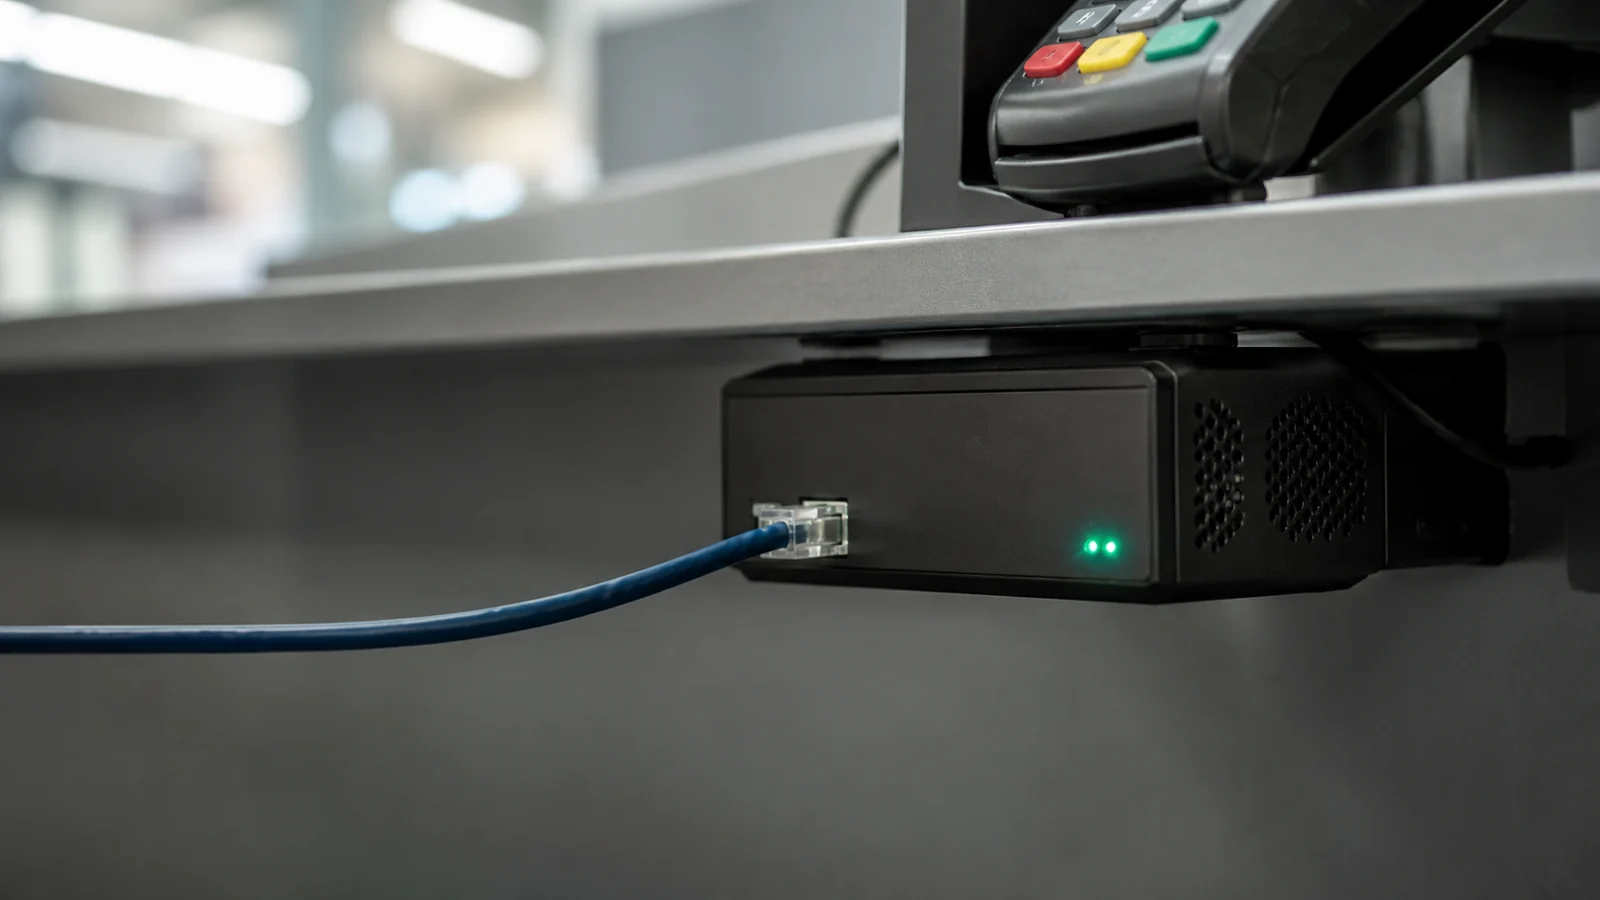
BREEZE COMET Hijacks Brazilian Payment Systems for Fraud
Mandiant traced BREEZE COMET from vishing, rogue branch hardware and stolen cloud credentials to payment APIs used for hundreds of fraudulent transfers.
Read article →Reader view
Choose the default article length.
Threat actors, malware campaigns, phishing, exploitation, and incident activity.
Mandiant traced BREEZE COMET from vishing, rogue branch hardware and stolen cloud credentials to payment APIs used for hundreds of fraudulent transfers.
Read article →Ten malicious npm releases used trusted publishing, two install-time launch paths, and a credential-stealing worm. Defenders must isolate hosts before rotating tokens.
Read article →CISA confirms exploitation of a critical Artifactory flaw and requires federal forensic triage. Self-hosted operators have six fixed-version floors to verify.
Read article →Fire Ant hid tunnels on Cisco routers, injected TACACS servers, and planted Linux backdoors. Sygnia's artifacts support checks of routers, authentication servers, and Linux hosts.
Read article →CISA confirmed exploitation of a 2019 SQL Server flaw and now requires affected systems to be patched after evidence preservation and forensic triage.
Read article →PaperCut confirms active exploitation of NG and MF servers. Release 3 patches the two-flaw chain; new log and service indicators help defenders investigate exposed hosts.
Read article →StopAndProtect turns hacked WordPress sites into malware hosts, command servers, and stores for stolen files before selective ransomware deployment.
Read article →Shadowserver's retrospective Dysphoria report identifies about 296,000 compromised IoT devices and gives network owners evidence to locate and rebuild affected systems.
Read article →Five newly fixed WordPress flaws expose conditional paths to admin takeover or server code execution; defenders should verify six component versions and review AJAX and account activity.
Read article →Citrix documents denial of service. Separate research demonstrates a SAML path to root code execution but has not confirmed that it maps to this CVE.
Read article →An exposed server revealed a repeatable Active Directory attack path, AI-assisted planning, Aurora lockers, and payment trails across multiple victims.
Read article →ErrTraffic lures lead users to run Cruciferra, which uses a vulnerable signed driver to terminate security processes before the Remus stealer runs.
Read article →Dindoor uses the signed Deno runtime, encoded stages, and a pre-persistence sandbox check. Hunt the fixed process and registry sequence beneath the changing payload.
Read article →Showing 79–91 of 156